
- cross-posted to:
- privacy@lemmy.ml
- cross-posted to:
- privacy@lemmy.ml
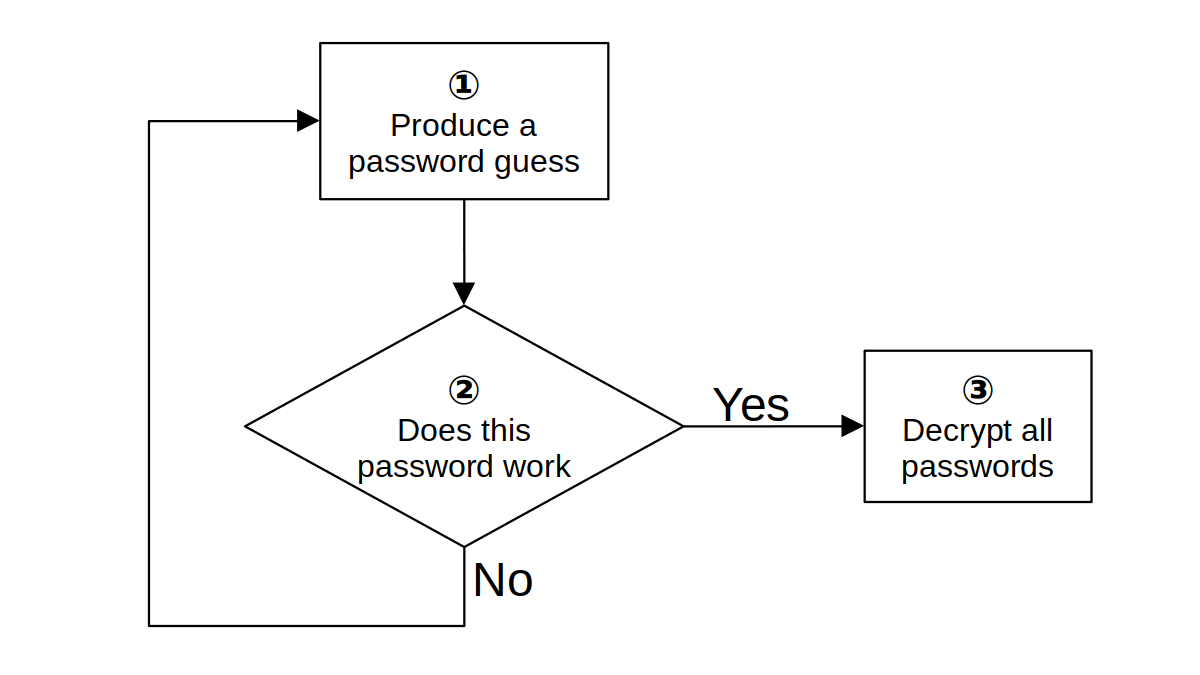
I try to explain how attackers would guess your password, should they get their hands on your encrypted data. There are some thoughts on the strength of real-world passwords and suggestions for your new password.
TL;DR XKCD solved this problem a decade ago, and somehow most of the industry still hasn’t caught up.
Still a good read, BTW.